> For the complete documentation index, see [llms.txt](https://help.cloudstoragesec.com/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://help.cloudstoragesec.com/how-it-works/integrations/aws-security-hub.md).
# AWS Security Hub CSPM
Antivirus for Amazon S3 and Data Classification for Amazon S3 both support AWS Security Hub CSPM.
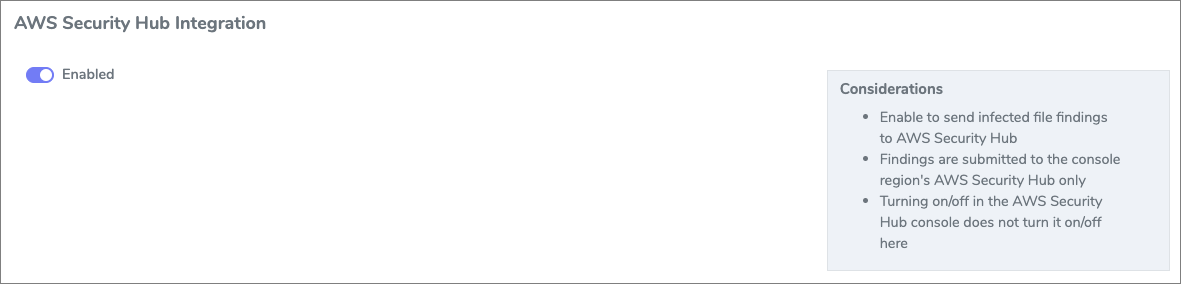
You can enable Security Hub CSPM by going to Configuration > AWS Integrations. Read on here for more information on implementing it.
AWS Security Hub CSPM provides a consolidated view of your security status in AWS. Automate security checks, manage security findings, and identify the highest priority security issues across your AWS environment. We have integrated with AWS Security Hub CSPM to allow your Amazon S3 object findings (infected files and data matching classified data patterns) to be posted to this central location. Any infected or matching files found within your Amazon S3 storage can be shown and managed alongside the rest of the findings coming from all other aspects of your infrastructure.
It is very simple to start sending infected or matching scan results to AWS Security Hub CSPM. Simply toggle the switch on (becomes purple and text changes from Disabled to Enabled) and we will activate Accept Findings inside of AWS Security Hub CSPM and immediately start sending findings. You will not have to manually accept, although you can, the findings service inside the AWS Console. If you accept the service beforehand, you will still need to enable the toggle in the management console.
## **Example Finding within AWS Security Hub** CSPM **Console**
## **Integration as seen inside the AWS Security Hub** CSPM **Console**
{% hint style="warning" %}
We expect AWS Security Hub CSPM to be subscribed to in the region the console is running within.
Any incident found, no matter the region, will be posted to the console region's AWS Security Hub CSPM. [Contact Us](/contact-us.md) if you'd like the findings written out to the region they were found in.
Flipping the toggle to enabled when AWS Security Hub CSPM is not subscribed to will be reflected with an error.
If you Stop Accepting Findings for our solution inside the AWS Security Hub CSPM console, but do not also disable it in the Console Settings page, we will continue to try to send events and errors will be sent to logs.
{% endhint %}
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://help.cloudstoragesec.com/how-it-works/integrations/aws-security-hub.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.