
Supported File Types
Below you can find the file types supported by each scanning engine that powers Antivirus for Amazon S3.
Antivirus for Amazon S3
Even if a file type is not on this list we will still attempt to scan the file byte for byte.
Data Classification for Amazon S3
Our data classification functionality supports scanning and classification of most text-based files. This includes the following:
TXT
DOC/DOCX
PDF
HTML
CSV
XLS/XLSX
XML
RTF
ODT
PPT/PPTX
Even if a file type is not on this list you can still upload it and attempt to classify it to see if it's supported.
Support for Archive Files
Our scanning engines support scanning files nested within archive files. The maximum supported archive depth depends on the scanning engine.
Supported Archive Depth
Sophos: Up to 5 levels of nested archives
ClamAV (CSS Secure): Up to 10 levels of nested archives
Bitdefender (CSS Premium): Up to 16 levels of nested archives
If a malicious file is detected within a nested archive, the entire parent archive is marked as infected and moved to the quarantine bucket.
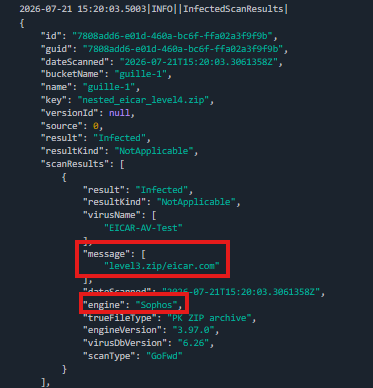
For Sophos, the scan result and object tags include a message identifying the file within the archive that was detected as malicious. For example, I uploaded a four-level nested archive containing an EICAR test file at level 3, and the scan result identified the infected file.
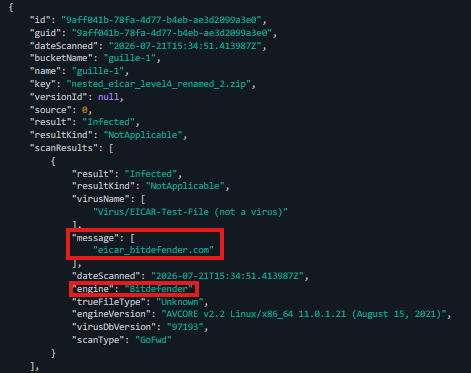
Bitdefender (CSS Premium) behaves similarly. The scan result includes a message identifying the infected file within the archive.
However, CSS Secure (ClamAV) cannot provide the same level of detail as Sophos or Bitdefender. In the Message section, the message will be empty, and the entire archive will be marked as infected. You will need to inspect the archive to determine which file within it is infected.
Last updated